Security Operations

The Brick House Special: From Data Overload to Decision-Driven Security

PARTNER SPECIAL ROUNDTABLE WEBINAR – CRIBL, GOOGLE CLOUD SECURITY, WIZ

Every new cloud workload, endpoint and AI agent adds another stream of security data. Visibility was the push for years — and most teams have made real progress there. The problem now isn’t seeing more; it’s that the signals, alerts, findings and vulnerabilities pile up faster than anyone can act on them.

Discussion topics:

  • Why visibility isn’t the bottleneck anymore
  • Using context to separate true signal from noise
  • What data to keep — and what to cut
  • Where agentic AI helps and where it just automates a broken process
  • Patch speed, “toxic combinations,” and defense in depth
  • Balancing prevention and detection as the attack surface shifts

GuidePoint Security CISO Gary Brickhouse sits down with security leaders from Cribl, Google Cloud and Wiz for a candid conversation on turning that flood of data into decisions. No slides. No demos. Just practitioners working through what actually holds up in production.

The panel:

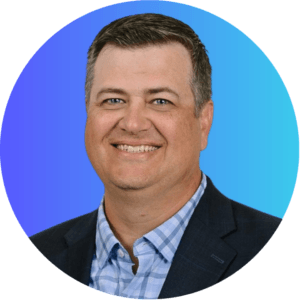
  • Gary Brickhouse — CISO, GuidePoint Security (host)
  • Myke Lyons — CISO, Cribl
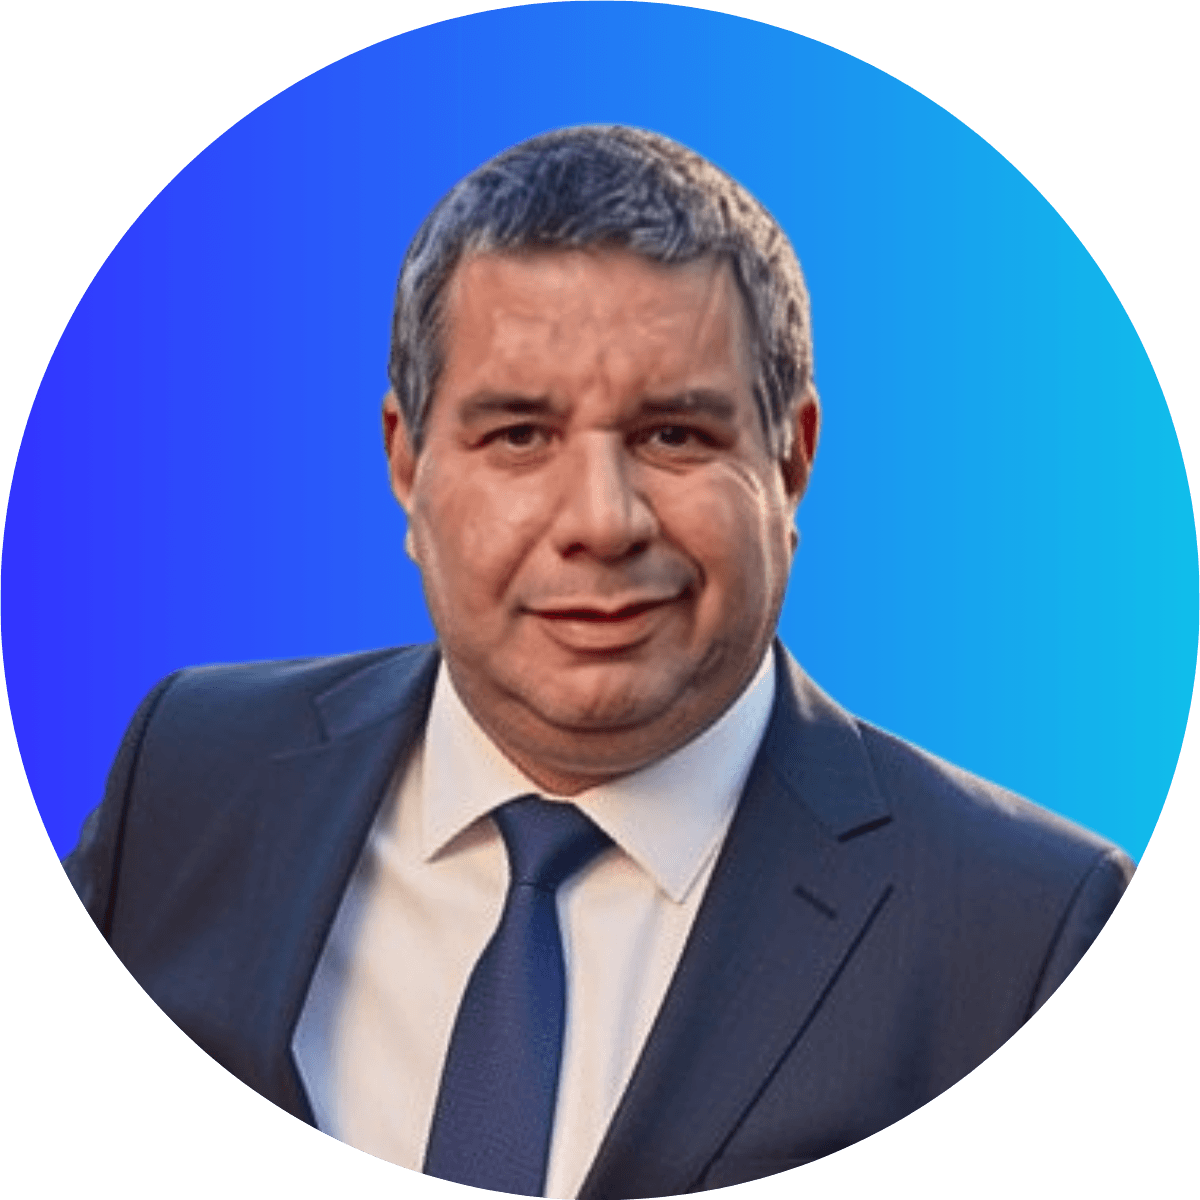
  • Adán Montoya — Enterprise Security Architect, Google Cloud
  • Ryan Kazanciyan — CIO/CISO, Wiz

Watch Now

Quotes from The Brick House #60

“We’ve got great visibility. Now we just have a ridiculous amount of data that’s flowing our way.”
— Gary Brickhouse, CISO, GuidePoint Security (~02:19)

“If a human cannot understand the data, the agent might not either, right?”
— Adán Montoya, Enterprise Security Architect, Google Cloud (~04:16)

“Even if there are the systems you can throw it all in there, it’s not really going to help you.”
— Myke Lyons, CISO, Cribl (~10:00)

“Not everything is preventable outright and detection plays a really important role to buy you time.”
— Ryan Kazanciyan, CIO/CISO, Wiz (~1:02:37)

EVENT SPEAKERS

Learn from Cybersecurity Experts

Gary Brickhouse
CISO, GuidePoint Security

Myke Lyons
CISO, Cribl

Adán Montoya
Enterprise Security Architect,
Google Cloud Security

Ryan Kazanciyan
CIO/CISO, Wiz

Inside the Episode

Because visibility has outpaced context. Most organizations can now see across their environment, but the raw volume of alerts, findings and vulnerabilities arrives without the context needed to tell a true positive from noise. Knowing what’s normal versus abnormal — and which asset or identity is involved — is what makes data actionable.

Add context before volume. Enriching events with asset criticality, identity and environment lets teams (and AI agents) separate real signal from noise, instead of drowning in low-value alerts. The same context that helps a human analyst triage is what an AI agent needs to act reliably.

No — collecting everything is no longer a sound strategy. Even platforms that can ingest petabytes a day don’t make “keep it all” worthwhile. Separate the use cases: detection, compliance retention and threat hunting need different data, retention windows and systems. Tier data by value and purpose.

Yes, when it closes the loop between finding and fixing. Specialized agents can collaborate — one validating vulnerabilities, another proposing and testing detections — freeing engineers for complex, poorly understood surfaces. The risk: teams that don’t use AI against their operational data are already behind attackers who do.

Toxic combinations are risk factors that are dangerous together even when each looks minor alone. Instead of scoring a vulnerability in isolation, you weigh the blend of exposure, identity risk, data risk and workload context. That combination is what surfaces the genuinely critical issues out of thousands of findings.

Treat the balance as something to re-check constantly, not set once. Not everything is preventable, so detection buys time and catches what isn’t yet well defined. Teams that over-trust their architecture — or lean too hard on the SOC to catch preventable issues — have the balance wrong.

Start with a pilot and don’t wait for perfect. The landscape moves too fast to wait for stability — pick one meaningful use case, use the free resources available and improve from there.